
Issue
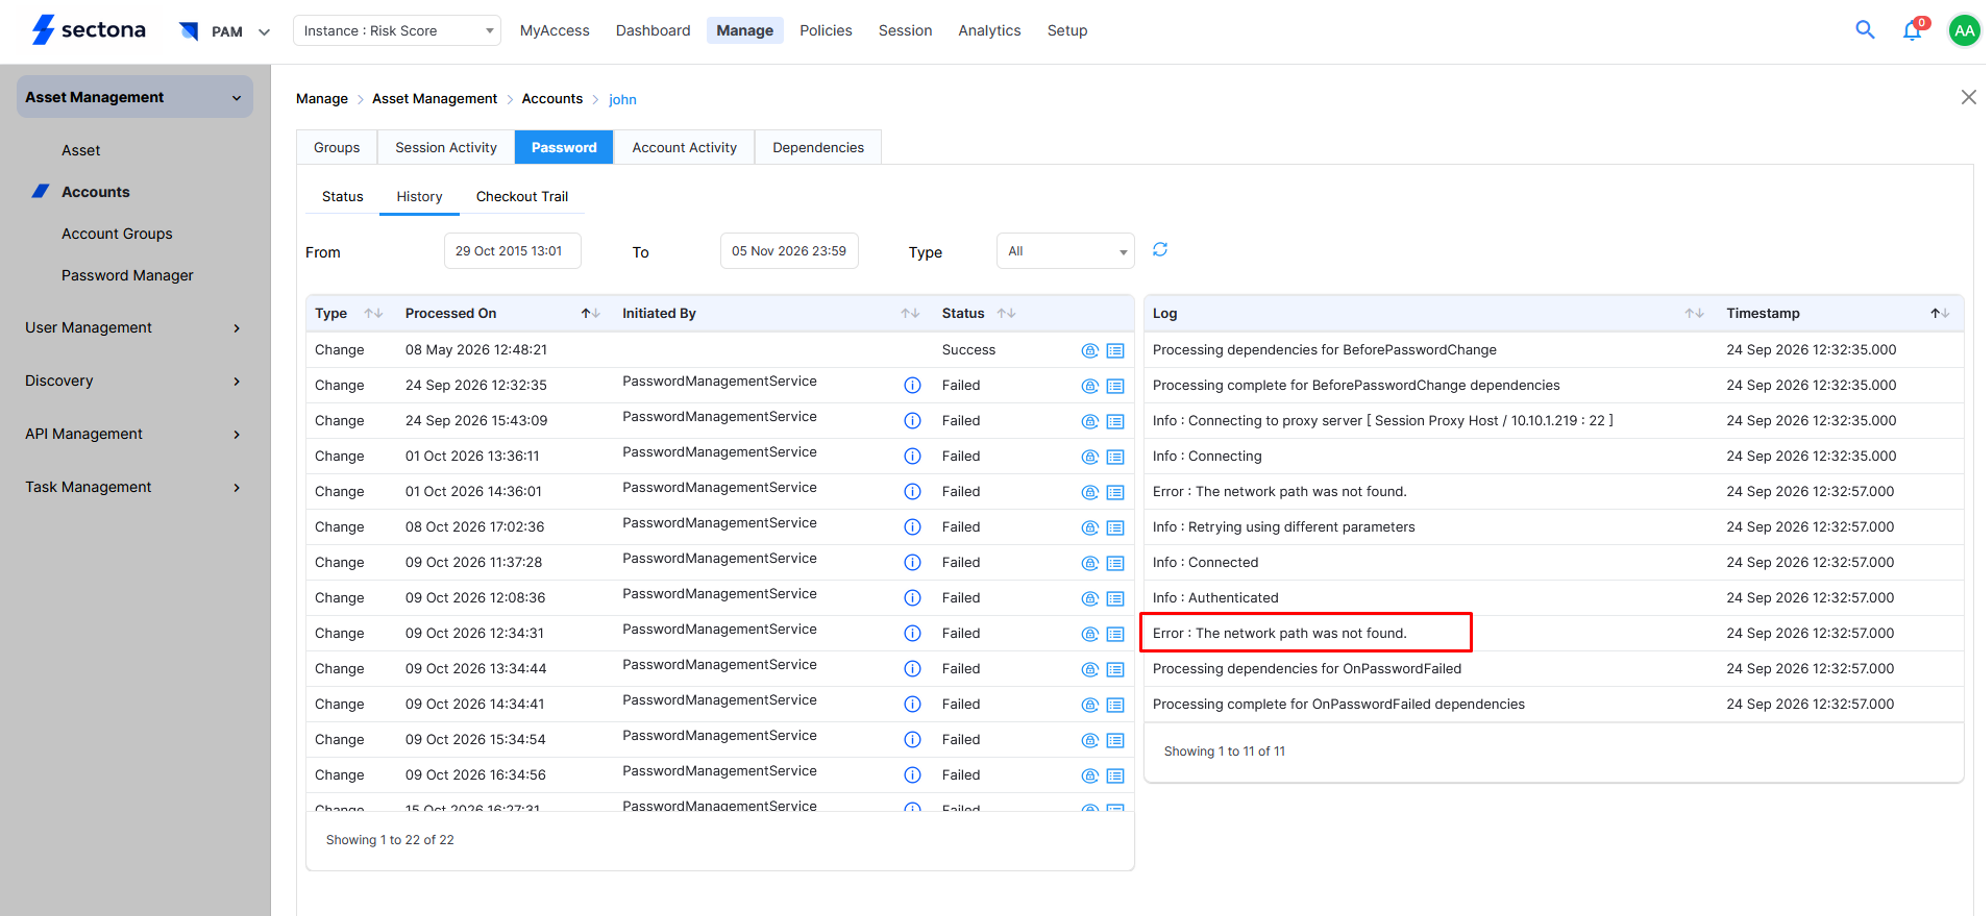
You may encounter an error while changing the password of a Windows server in a workgroup environment.
Error: “Access is denied. The network path was not found.”
Cause
This error may occur due to any of the following reasons:
-
Case 1: Port 445 (SMB) is blocked between the PAM Web Access server and the target Windows server.
-
Case 2: The following User Account Control (UAC) policies are enabled on the target Windows server:
-
User Account Control: Admin Approval Mode for the Built-in Administrator Account
-
User Account Control: Run All Administrators in Admin Approval Mode
-
-
Case 3: The “LMCompatibilityLevel” setting on the target Windows server is incompatible with the required authentication configuration.
Resolution
Case 1: The Sectona PAM Web Access server must open the following ports to all target Windows servers:
|
Source |
Destination |
Port |
|
Sectona PAM Web Access server |
All target Windows servers |
445 (NetBIOS) |
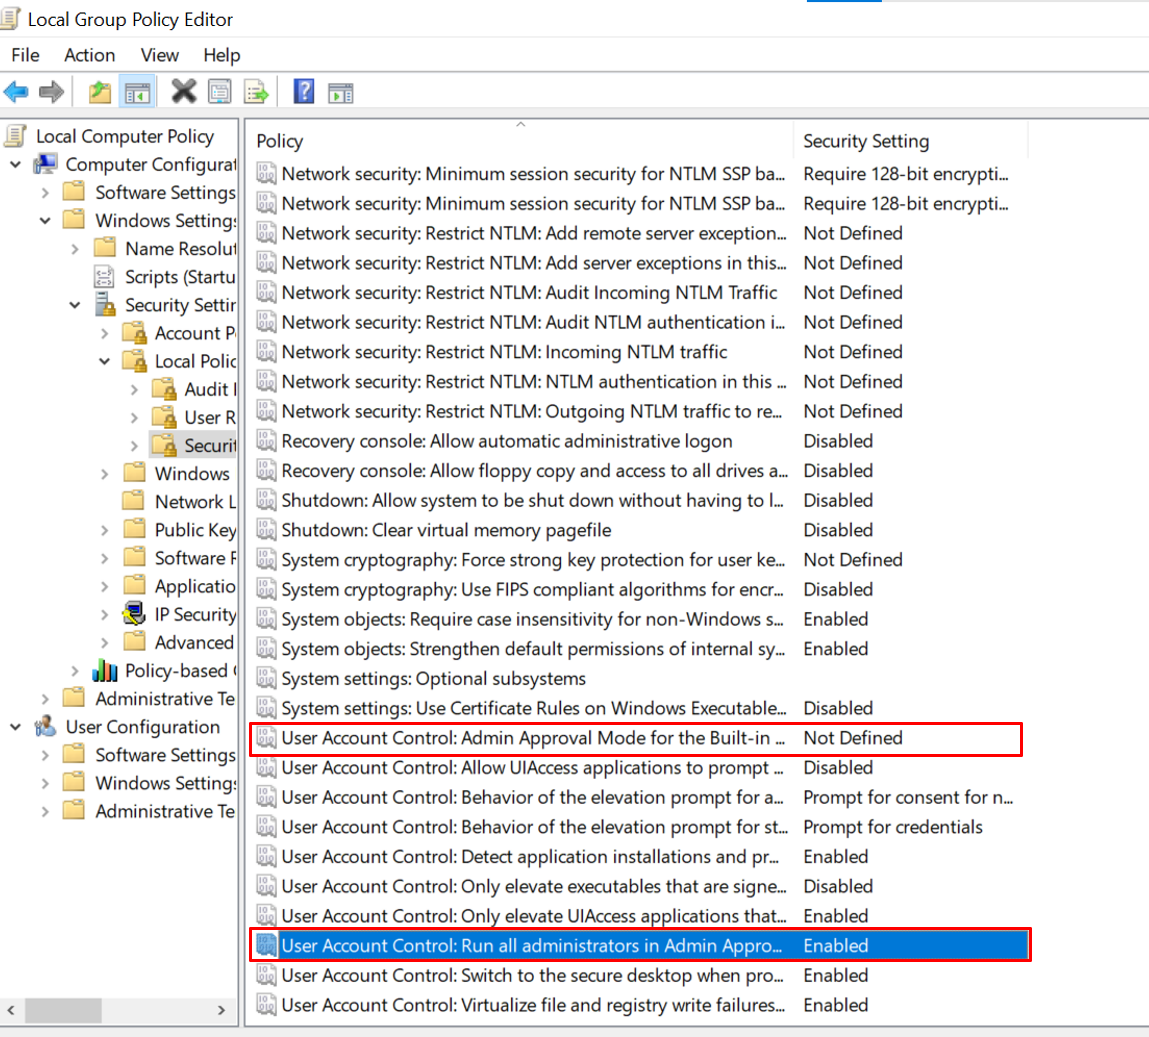
Case 2: Disable the following Local Computer Policies on the target Windows server to allow the PAM application to connect to the target server and reset passwords of privileged accounts:
-
-
User Account Control: Admin Approval Mode for the Built-in Administrator Account
-
User Account Control: Run All Administrators in Admin Approval Mode
-
If these policies are originally enabled, a system restart may be required after disabling them to ensure that the changes are applied properly.To disable these policies:
-
On the target Windows server, open the Run dialog (Windows+R), enter gpedit.msc, and press Enter.
-
Navigate to Computer Configuration → Windows Settings → Security Settings → Local Policies → Security Options.
-
Open the two policies as shown in the image below.
-
Select Disabled, click Apply, then click OK.
-
Restart the target server if required for the changes to take effect.
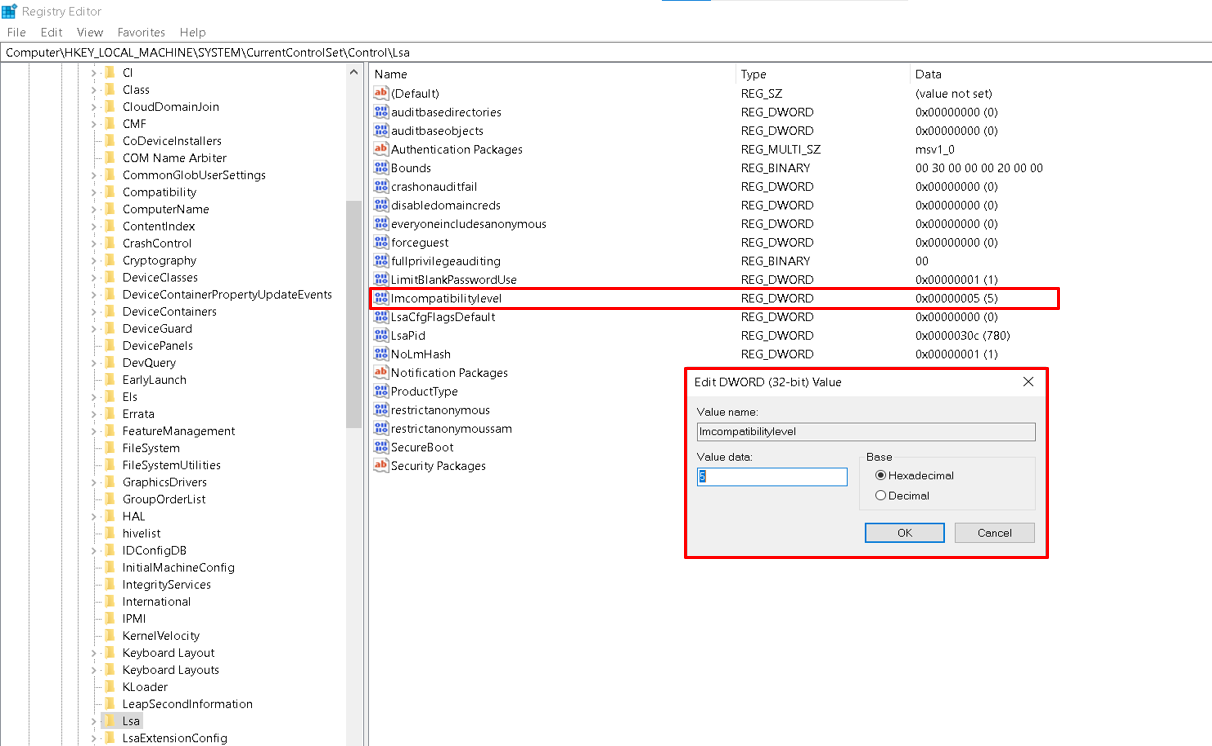
Case 3: If a hardening policy is enforced across all Windows servers and specifies the “LMCompatibilityLevel” ensure that the same “LMCompatibilityLevel” value is configured on all target Windows servers and the Sectona Web Access server.
To check the “LMCompatibilityLevel”value:
-
Open the “Registry Editor” on the server.
-
Navigate to the following registry path:
“HKEY_LOCAL_MACHINE -> SYSTEM -> CurrentControlSet -> Control -> Lsa -> LmCompatibilityLevel”
-
Locate the “LMCompatibilityLevel” registry entry and check its configured value.
-
Ensure that the value is consistent across the target Windows servers and the Sectona Web Access server.
-
If the “LMCompatibilityLevel” value differs across Windows servers, configure the same value on all target Windows servers and the Sectona Web Access server.
-
If no hardening policy enforces a specific “LMCompatibilityLevel”configuration, you can either set the registry value to 0 to disable the policy or delete the “LMCompatibilityLevel” registry entry from the server.